The IoT Security Challenge
As industrial facilities deploy thousands of IoT devices—sensors, cameras, controllers, wearables—the attack surface expands dramatically. Each device represents a potential entry point for malicious actors. Unlike traditional IT systems, industrial IoT operates in environments where a security breach could have physical consequences: production shutdowns, safety incidents, or equipment damage.
Unique Industrial IoT Challenges
Legacy Systems and Long Lifecycles
Industrial equipment often operates for decades. Many systems were designed before cybersecurity was a consideration. These legacy devices can't be easily updated or replaced, yet they must coexist with modern IoT infrastructure.
Resource-Constrained Devices
Many IoT sensors have limited processing power, memory, and battery life. Traditional security approaches designed for servers or workstations don't translate well to these constrained devices.
Operational Continuity Requirements
Manufacturing processes can't afford downtime for security patches or system updates. Security measures must work around production schedules, sometimes requiring creative solutions to maintain both security and uptime.
Zero Trust Architecture
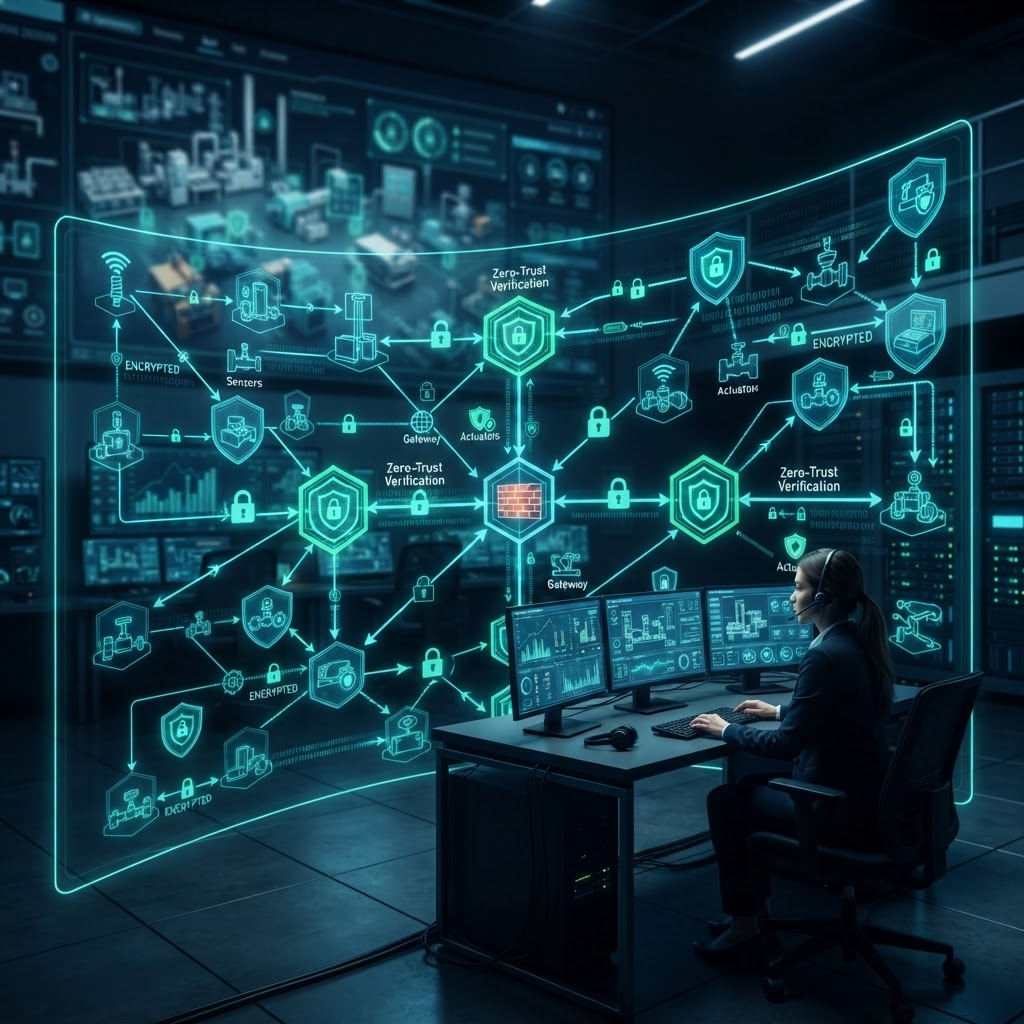
The foundation of modern IoT security is zero trust: never trust, always verify. Every device, user, and data flow must be authenticated and authorized. Network segmentation isolates devices into security zones. Micro-segmentation limits lateral movement. Continuous monitoring detects anomalies in real-time.
Defense in Depth
No single security measure is sufficient. Effective IoT security requires multiple layers: secure device provisioning and authentication, encrypted communications end-to-end, network segmentation and access controls, continuous monitoring and threat detection, regular security updates and patch management, and incident response procedures.
Private Networks for Security
Private 5G networks provide inherent security advantages. All traffic stays on-premises, never traversing public internet. SIM-based device authentication ensures only authorized devices connect. Network slicing provides isolation between different applications and security zones.
Operational Best Practices
Maintain an accurate inventory of all IoT devices. Implement default-deny security policies. Use strong, unique credentials for each device. Segment networks based on security requirements. Monitor for unusual behavior patterns. Have an incident response plan. Regularly test security controls. Train staff on security awareness.
The Path Forward
IoT security is not a one-time project but an ongoing process. As threats evolve, security measures must adapt. Organizations that build security into their IoT deployments from the beginning—rather than bolting it on afterward—will be best positioned to realize IoT's benefits while managing its risks.
The future of industrial operations is connected. With thoughtful security architecture and disciplined operational practices, organizations can embrace this connectivity confidently and securely.
By Badrinath Kodandarama